
A risk committee exists to take decisions that nobody in operations should take alone: accepting a risk close to the limit, paying to reduce it, transferring part of it or abandoning the activity that creates it. This guide shows how the committee organises that work, from its charter to the record of each decision, and where AI-prepared analysis helps without taking accountability for the choice away from people.
This blog has already covered neighbouring topics. The post on the decision intelligence platform for risk explains the technology layer that consolidates the data, AI risk analysis: from data to decisions shows how that data becomes priorities, and How the CISO should report cyber risk to the board deals with the format of board reporting. The focus here is how the committee itself works: how it is set up, how it prepares and runs the meeting, how it decides and how it documents each decision.
What a risk committee does, according to the references
COSO ERM, in its 2017 version (Integrating with Strategy and Performance), opens its 20 principles with board risk oversight: the board oversees strategy and carries out governance responsibilities to support management (principle 1). Further on, the organisation identifies and selects risk responses (principle 13) and reviews performance while considering risk (principle 16) (COSO, executive summary, June 2017). In many organisations the risk committee is the forum where those principles turn into a meeting, an agenda and minutes.
In the Brazilian financial system, the committee is mandatory. CMN Resolution No. 4,557/2017 requires institutions authorised by the Central Bank of Brazil (BACEN) in segments S1 to S4 to maintain a risk management framework and, under art. 45, to set up a risk committee. S4 institutions are exempt from setting one up (art. 60), and S3 institutions are exempt from the independence requirements in §§ 4 to 6 (art. 59) (CMN Resolution No. 4,557/2017). Under art. 45, § 1, the committee's duties include:
- Making recommendations to the board of directors, at least once a year, on risk management policies, strategies and limits, among other matters in art. 48, item II.
- Assessing the risk appetite levels set in the Risk Appetite Statement (RAS) and the strategies to manage them, looking at risks individually and in an integrated way.
- Overseeing the work and performance of the chief risk officer (CRO).
- Overseeing executive management's compliance with the RAS.
- Assessing how closely risk management processes follow the established policies.
- Keeping records of its deliberations and decisions.
The rule also sets the composition. The committee has at least three members (§ 2). Most of them cannot have been employed by the institution in the last six months, cannot receive any other pay from it beyond their fees as committee or board members, must have proven risk management experience and cannot hold control or take part in executive decisions (§ 5). Nobody who was CRO or a member of the audit committee in the last six months can sit on the committee (§ 4), and the chair cannot have chaired the board or any other committee of the institution in that period (§ 6). The committee coordinates with the audit committee (§ 7), and its composition and duties must be published on the institution's website (art. 57).
Outside institutions authorised by the Central Bank, whether a committee is required depends on the sector and the regulator. Where there is no specific rule, the committee is a governance choice, and Resolution 4,557 is a useful design reference even where it does not apply.
The charter: what needs to be written down
Resolution 4,557 does not set a meeting frequency. It requires the internal regulations, or an equivalent document, to deal expressly with the maximum number of members, the operating rules, including duties and minimum meeting frequency, how the committee reports to the board and the length of members' terms, where set (art. 45, § 3). In practice, a charter that works usually also answers these questions:
- Authority: what the committee decides and what it only recommends. In financial institutions, it is the board that sets appetite in the RAS and authorises exceptions to policies, limits and appetite levels (art. 48, items I and VI). The committee assesses and recommends.
- Quorum and voting: how many members must be present, how votes are taken and how reservations are recorded.
- Conflicts of interest: how a member declares a conflict and abstains on the item.
- Deadlines: how many days in advance the pre-read is sent and how quickly the minutes and decision log are circulated.
- Private session: Resolution 4,557 requires conditions for the CRO to report to the committee directly and without executive directors present (art. 44, § 4). Building that slot into the agenda means it does not depend on an ad hoc request.
The pre-read: the pack that arrives before the meeting
A good meeting starts days earlier, with a pack members can actually read. Resolution 4,557 lists what management reports to executives, the committee and the board must cover (art. 7, item X): aggregate risk exposure and its main drivers, adherence to the RAS and limits, an assessment of systems and routines including any weaknesses and the actions to fix them, mitigation actions and their effectiveness, how widely risk culture has spread, and the assumptions and results of stress tests. In financial institutions, the annual cyber security report required by CMN Resolution No. 4,893/2021 also goes to the risk committee before it is presented to the board (art. 8, § 2).
A practical way to organise the pack is to split it in two:
- Overview: the usual stable indicators, shown as trends, with what has changed since the last meeting. The format of those indicators is covered in the posts on reporting risk to the board and on KRIs.
- Decision items: one paper per topic, with the risk and its owner, the current position against appetite and tolerance, the response options with the cost and expected residual risk of each, the risk function's recommendation and what happens if nothing is done before the next meeting.
Each paper should say where the numbers come from and what is missing. Resolution 4,557 requires the board, the committee, the CRO and executive management to understand the limitations of the information in the reports and the uncertainties of the models and methodologies used, even when developed by third parties (art. 51, items II and IV). A pre-read that hides data gaps undermines exactly that understanding.
Agenda: separating updates from decisions
The most common mistake is spending the meeting on presentations and leaving the decisions for the last ten minutes. An agenda that protects decision time usually follows this order:
- Opening, quorum and declaration of conflicts of interest.
- Follow-up on previous decisions, read straight from the decision log: what was done, what is late, what needs a new resolution.
- Decision items, from the most consequential to the least.
- Significant changes in the risk profile since the last meeting, such as a new regulation, an incident, an acquisition or a critical supplier (COSO covers this in principle 15, on assessing substantial change).
- Updates, read in advance and discussed only if a member asks.
- Private session with the CRO.
- Matters to escalate to the board.
The four responses and the appetite test
Every decision item ends in a response. NIST, in IR 8286 Rev. 1 (December 2025), notes that terminology varies between frameworks and sums up the responses to negative cyber security risks in four types (NIST IR 8286r1, section 3.5):
- Accept: for risks within tolerance levels. No further action beyond monitoring.
- Transfer: for risks outside tolerance, share part of the consequences with another party, as with cyber insurance. NIST points out that some consequences cannot be transferred, such as the loss of customer trust.
- Mitigate: apply actions, such as security controls, that reduce threats, vulnerabilities and impacts to an acceptable level.
- Avoid: apply responses that ensure the risk does not occur, for example by not carrying out the activity that creates it. It may be the best option when there is no cost-effective way to reduce the risk, but the cost of the lost opportunity has to be weighed.
The test for choosing between them is the comparison with the approved appetite and tolerance, which the NIST CSF 2.0 expects to be established and communicated (subcategory GV.RM-02) (NIST CSWP 29). Three questions help the committee apply it:
- Is the current risk within tolerance? If so, accepting it with monitoring is a legitimate response, provided it is recorded.
- If not, which option brings residual risk within tolerance at the lowest cost? IR 8286 suggests exploring avoidance when the cost of the response exceeds the benefit of the activity at risk.
- Does the response create new risks? The NIST example is multi-factor authentication, which reduces an access risk and may create another one, lower productivity.
The comparison is easier to defend when appetite stops being a sentence and becomes a measurable limit, as the post Risk appetite: from sentence to number shows, and when options are compared in ranges of financial loss, the subject of the post on Cyber Risk Quantification (CRQ). IR 8286 itself encourages quantifying risk in financial terms wherever feasible. Accepting a risk above appetite is not acceptance but an exception, and in financial institutions exceptions to the appetite levels in the RAS are authorised by the board (art. 48, item VI, of Resolution 4,557).
The decision log
The minutes summarise the meeting; the decision log keeps each decision in a form that can be looked up, followed up and audited later. For the committee of a financial institution, keeping records of deliberations and decisions is an explicit duty (art. 45, § 1, item VI). NIST IR 8286 Rev. 1 offers a good set of fields: the risk register holds the response type, cost, response description, risk owner and status, and the risk detail record adds the people involved in response decisions, the dates of the last and next assessment, and the decisions taken with their follow-up. A template, with a hypothetical example:
| Field | What to record | Hypothetical example |
|---|---|---|
| Identification | Decision number, date and meeting | DEC-2026-014, November ordinary meeting |
| Risk and owner | One-sentence scenario and who is accountable for it | Payments system outage caused by ransomware; owner: chief operating officer |
| Position against appetite | Estimated exposure, approved limit and headroom or excess | Estimated loss range above the tolerance approved for the process |
| Options assessed | Responses considered, with the cost and residual risk of each | Mitigate (segmentation and immutable backup); transfer part (insurance); accept |
| Decision | Response chosen | Mitigate and transfer part of the financial impact |
| Rationale | The deciding criterion and why the other options were rejected | Accepting would require an exception to appetite; insurance alone does not cover the loss of customer trust |
| Target residual risk | Where the risk should end up and by when | Within tolerance in two quarters |
| Actions | Each action with an owner and a date | Segmentation: IT, by March; policy: finance, by January |
| Inputs | Pre-read and analyses used, including whether any analysis was prepared by AI and who reviewed it | Risk function paper; prioritisation suggested by the platform, reviewed by the CRO |
| Votes and reservations | Unanimity or dissent, with the reason | Approved, with one reservation on the segmentation deadline |
| Escalation | Whether the item goes to the board and why | Inform the board at its next meeting |
| Review | Date or trigger for the item to return to the agenda | In May, or earlier if a key risk indicator for the process breaches its limit |
Two habits make the log useful. First, every acceptance has an expiry date and a review condition; an acceptance without a date turns into oblivion. Second, the rationale must be written on the day, with the criterion used. Months later, it is the only way to show an auditor or a new member why two similar risks were treated differently, or the same.
Follow-up: a decision is only finished when the risk changes
Once a response is approved, IR 8286 Rev. 1 describes the next step: update the register with the accountable owner, compare residual risk with appetite and tolerance, decide whether any further response is needed and communicate the decisions to risk owners in a timely way. In the committee, this becomes a few simple routines:
- Follow-up on the decision log is a standing agenda item, right at the start.
- Late actions have an escalation rule set in the charter, rather than depending on the chair's memory.
- Expired acceptances return to the agenda automatically.
- Key risk indicators act as triggers: when a limit is breached, the item returns before its scheduled date.
- At least once a year, the committee consolidates its recommendations to the board, as art. 45, § 1, item I, of Resolution 4,557 requires.
This follow-up only stays light if risk management runs continuously between meetings, with owners and status updated week by week. That is the argument of the post on the CROC, the Cyber Risk Operations Center.
Where AI-prepared analysis fits, and where it does not
AI helps more in preparation than in the room. Used with human review, it can:
- Consolidate risk, control and exposure data and flag what has changed since the last meeting.
- Draft decision papers, with the four options and the position of each against appetite.
- Suggest a response and an estimate of residual risk, making clear which data it started from.
- Compare the item with earlier decisions in the log and flag inconsistencies.
- Draft the minutes and update the decision log after the meeting, for the secretary to review.
What it does not do is decide, set appetite or take on accountability. The NIST CSF 2.0 places responsibility and accountability for cyber security risk on organisational leadership (GV.RR-01), and Resolution 4,557 requires the board, the committee, the CRO and executive management to understand the limitations and uncertainties of the models used, including third-party ones (art. 51, item IV). For a committee, that calls for three habits: asking, for every AI suggestion, which data it used and what was left out; recording in the log when AI-prepared analysis was used and who reviewed it; and keeping the prepared recommendation and the final decision side by side, so that differences are visible. Governing the models themselves is the subject of the post on AI governance software.
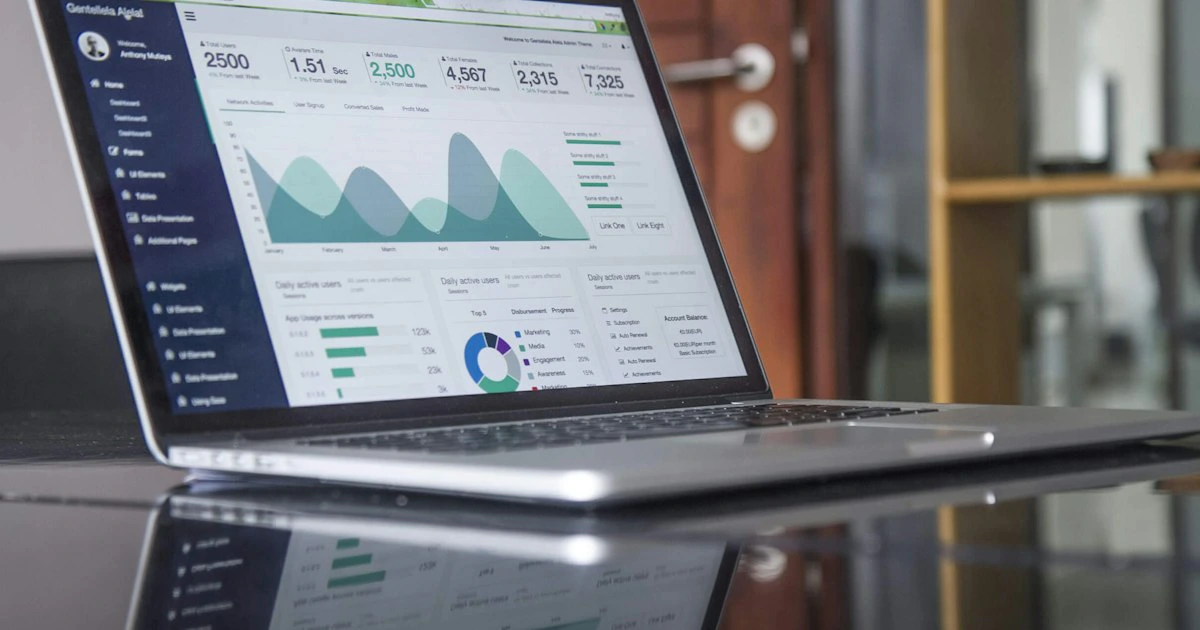
Futture's Eagle was designed along these lines. The AI suggests priorities, recommendations and executive summaries, and the user reviews, approves, rejects or adjusts every relevant result; the aim is for each recommendation to keep its context, data source, rationale, confidence level and decision history. The enterprise risk module brings together appetite, tolerance and indicators, treatment plans and board dashboards.
Conclusion
Before the next meeting, do three things. Reread the charter and check that it says clearly what the committee decides and what it recommends, with what quorum and to what deadlines. Turn each decision item on the agenda into a paper with the four options and the position of each against appetite. And open the decision log with what was decided at the last meeting, with an owner, a deadline and a review date. With those three documents, AI has something to work on and the committee can show, at any time, who decided what and why.
Further reading: Risk appetite: from sentence to number; KRIs: key risk indicators every CISO should monitor; Decision Intelligence Platform for Risk.
Frequently asked questions
Is every company required to have a risk committee?
No. In Brazil, CMN Resolution No. 4,557/2017 requires a risk committee in institutions authorised by the Central Bank of Brazil in segments S1 to S3; S4 institutions are exempt. In other sectors it depends on the regulator, and where there is no rule the committee is a governance choice.
Which responses can the committee choose from?
As NIST IR 8286 Rev. 1 puts it, there are four: accept the risk within tolerance, transfer part of the consequences, mitigate with controls or avoid the activity that creates the risk. The choice is made by comparing current and expected residual risk with the approved appetite and tolerance.
What should the committee's decision log contain?
The risk and its owner, the position against appetite, the options assessed, the decision, the rationale, the target residual risk, actions with owners and deadlines, the inputs used, votes and reservations, escalation to the board and the review date or trigger.
Can AI take the decision instead of the committee?
No. AI can prepare the pre-read, suggest responses and draft the minutes, but the decision and the accountability belong to the committee. In financial institutions, CMN Resolution No. 4,557/2017 requires the committee to understand the limitations and uncertainties of the models used, including third-party ones.
Official references
- CMN Resolution No. 4,557/2017 — Central Bank of Brazil
- CMN Resolution No. 4,893/2021 — Central Bank of Brazil
- COSO — Enterprise Risk Management: Integrating with Strategy and Performance, executive summary (2017)
- NIST IR 8286 Rev. 1 — Integrating Cybersecurity and Enterprise Risk Management (ERM), December 2025
- NIST Cybersecurity Framework 2.0 (NIST CSWP 29)
About the author
Founder, Futture.ai | CISSP
Cybersecurity, governance and risk management specialist with over 25 years of industry experience. CISSP-certified, founder of Network Secure and Futture.ai.